Ensure no security groups allow ingress from 0.0.0.0:0 to port 22
= Checkov/CKV_AWS_24 main.tf:7 Ensure no security groups allow ingress from 0.0.0.0:0 to port 22rossedman/sarifix
Point sarifix at Trivy, Checkov, golangci-lint or your own tool with one config file. It tracks every finding by a stable fingerprint, and will only ship a fix a rescan proves.
go install github.com/rossedman/sarifix/cmd/sarifix@latest
The problem
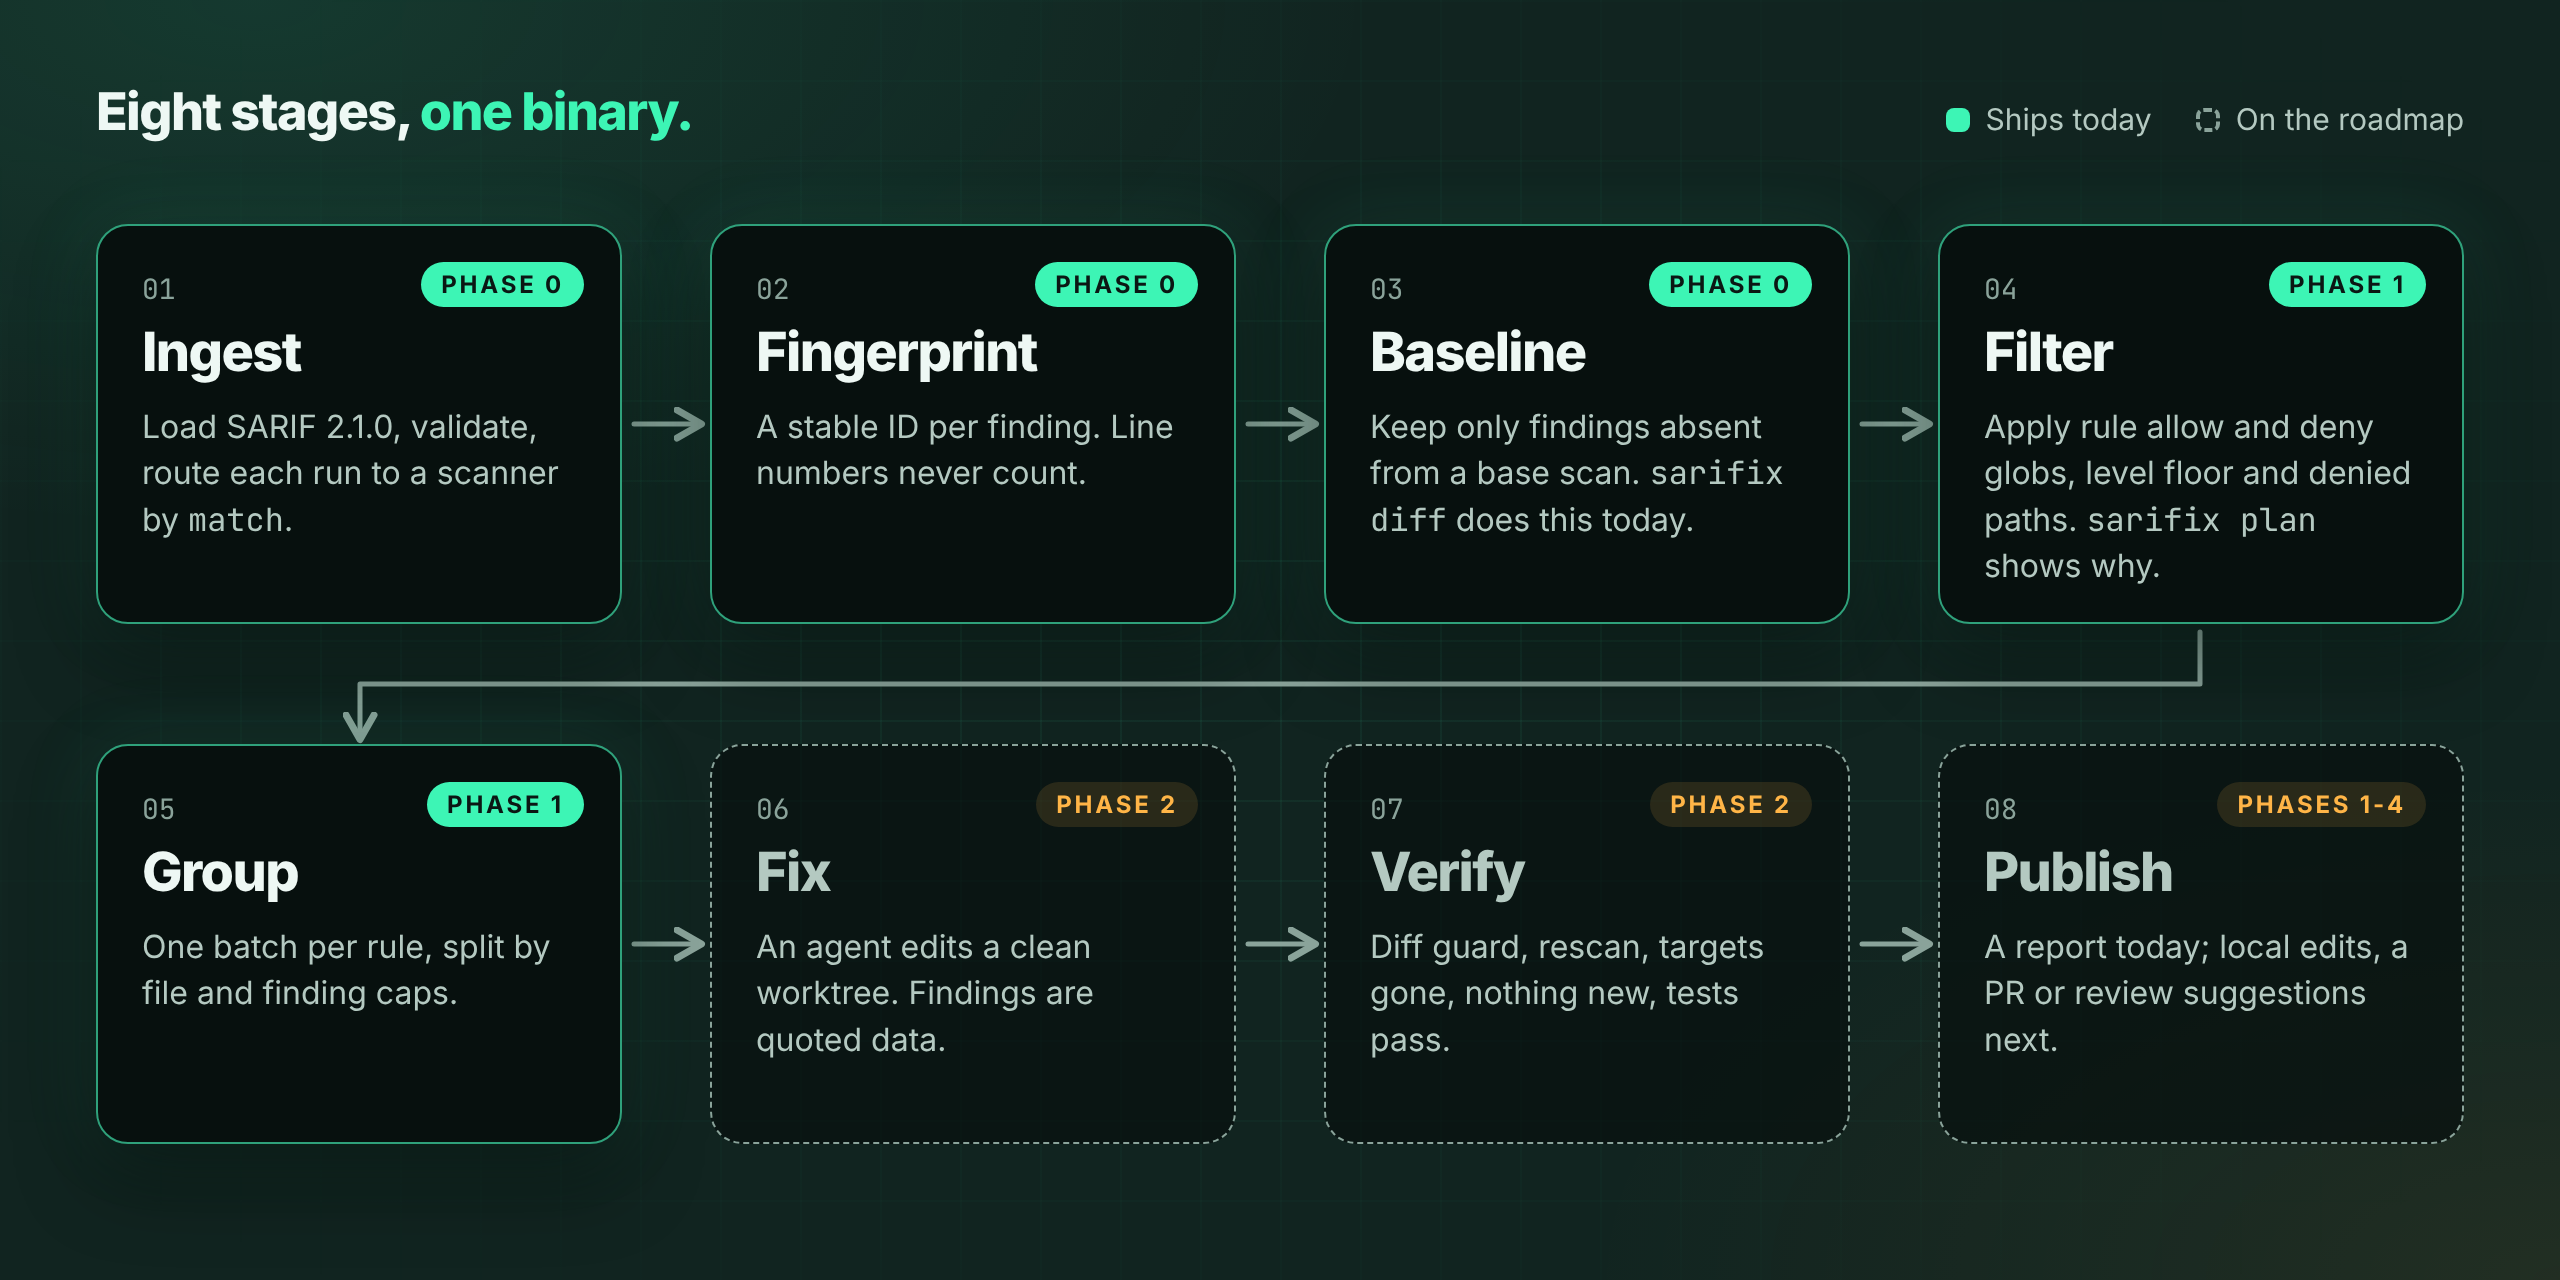
A scanner reports hundreds of findings, and the numbers only grow. Matching today's report to last week's breaks as soon as someone adds a line above a finding. sarifix gives every finding an identity that survives edits, so you can say what is new, what is fixed and what is unchanged.
= Checkov/CKV_AWS_24 main.tf:7 Ensure no security groups allow ingress from 0.0.0.0:0 to port 22Core ideas
Scanners are entries in a YAML file. Identity comes from fingerprints. Trust comes from verification, which arrives with the fixing phases.
A name, the SARIF tool names to match, and a command. No code change to add a tool.
- name: checkov
match: ["Checkov"]
command: ["checkov", "-d", "{dir}",
"-o", "sarif",
"--output-file-path", "{outdir}"]
The tool's own hash if it has one, otherwise a hash of tool, rule, path and the flagged code.
partialFingerprints:
sarifix/v1: fcadca11a498b6d6…
line numbers never count
A fix ships only if the rescan shows the finding gone, nothing new, and your tests pass.
verify:
commands: [["make", "test"]]
require_no_new_findings: true
Why sarifix
Four SARIF producers are tested in the fixture, one of them a 25-line shell script. A new tool is one scanners entry.
Line numbers never count, and edits inside a flagged resource don't change the identity of its other findings.
28 load-time checks. Each error names the file, the key path and the line. Exit code 2 means a config error.
.github/workflows/** is always in paths.deny, however you layer your config.
Planned: no change is published unless a rescan and your own tests pass. Nothing is ever auto-merged.
Put org defaults under a repo file with --org-config. Scanners and campaigns merge by name; the repo wins.
Quick start
You need Go 1.27 or newer, and whichever scanners your config calls on your PATH. Release binaries are signed with cosign if you prefer those.
Full getting-started guide$ go install github.com/rossedman/sarifix/cmd/sarifix@latest
Start from the example in the repo and validate it.
$ sarifix config validate --config examples/sarifix.yaml
One SARIF file per scanner, each result fingerprinted.
$ sarifix scan
Documentation